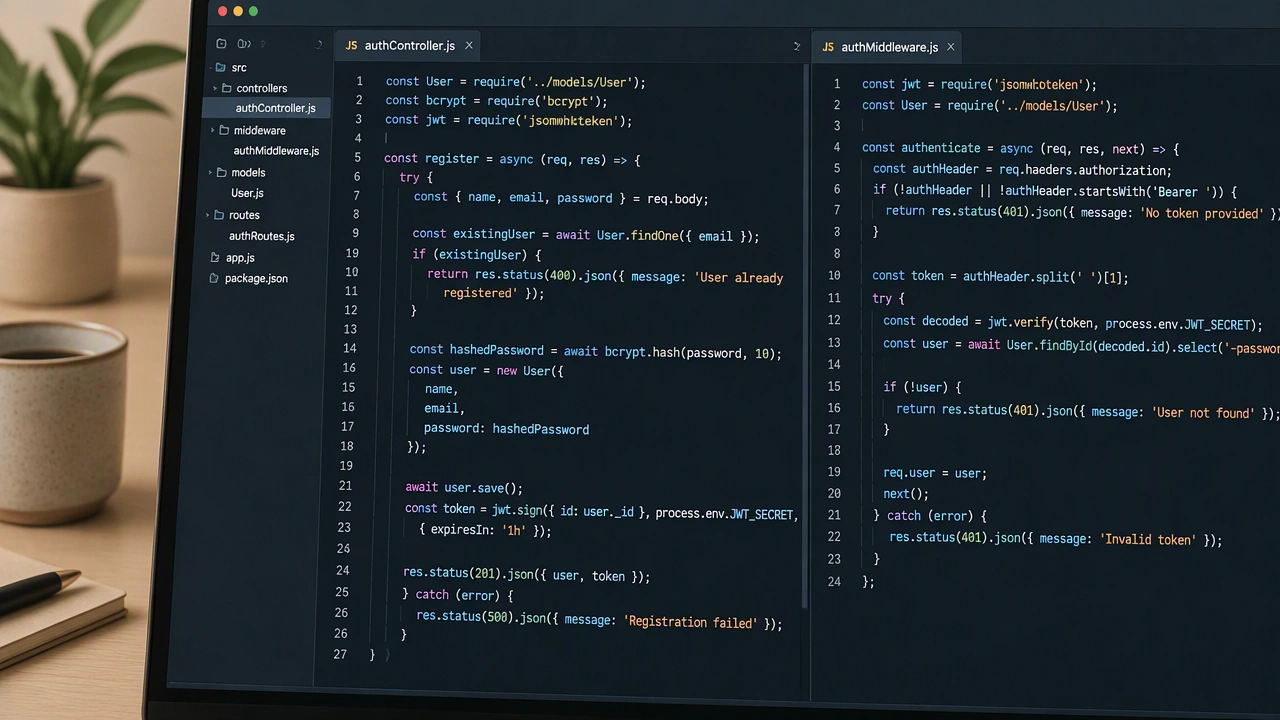
I’ve written a JWT-based authentication middleware for my Express.js application and would love some feedback before merging it into the main branch. The middleware handles token verification, role-based access control, and refresh token rotation. I’m particularly concerned about the security implications of my token storage strategy and whether my error handling covers edge cases properly. The code is roughly 200 lines and includes rate limiting on the login endpoint. I want to make sure I’m not introducing vulnerabilities like timing attacks during token comparison or leaving paths unprotected. If you’ve reviewed auth systems before, I’d especially appreciate comments on the refresh token logic and how I’m handling token revocation for logged-out users.